
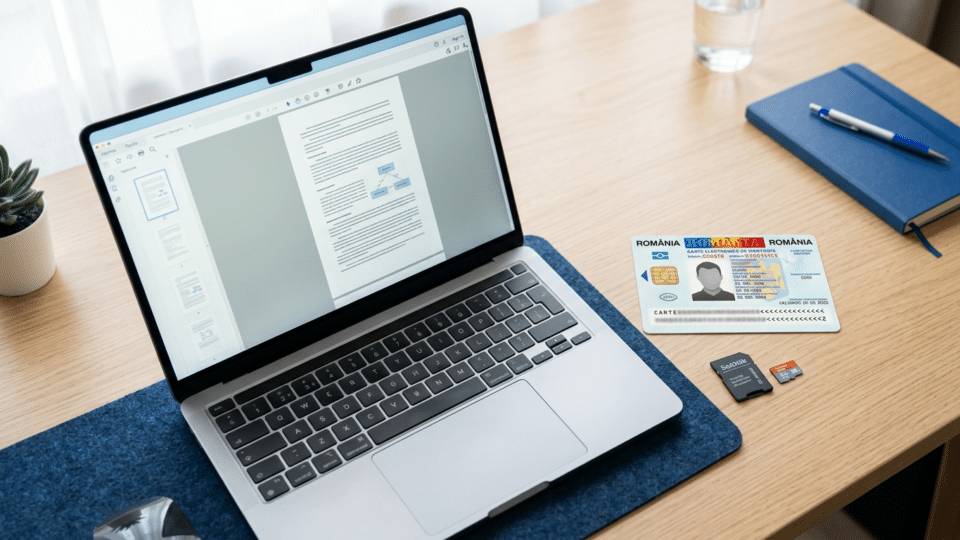
A PDF signed using the electronic-signature certificate on Romania’s electronic identity card (CEI) can be checked through the dedicated service on the Interior Ministry’s HUB MAI portal. In the public interface consulted, the service accepts PDF files only, up to 20 MB. Upload the original document, not a scan or a version saved again after signing.
In brief: a valid result is an important technical confirmation for the file checked. It does not, however, guarantee that the document has been completed correctly, includes all attachments, was issued by someone authorised to do so in a given context, or will be accepted by the receiving institution through the chosen channel.
Verifying a CEI electronic signature: steps on HUB MAI
Go to the Interior Ministry service for checking documents signed with a CEI. This is the indicated route for signatures applied with the certificate on the electronic identity card, rather than a validator presented as universal for every type of electronic certificate.
- Keep the received or signed PDF in its original form. Do not open and save it again in a PDF application, convert it to another format, or print and scan it before checking it.
- Check the file size. The HUB MAI page states a 20 MB limit. If the PDF exceeds that limit, do not try to “fix” it by saving it again without understanding the effect on the signature; ask the sender for the original version or, where the procedure allows it, for a document with its attachments sent separately.
- Upload the PDF to the dedicated CEI service. Select precisely the document you intend to send on.
- Keep the displayed verdict and the checked version. For an important file, save the original PDF separately and note the date it was checked. If the portal provides a downloadable result or a verification identifier, keep it with the document.
- Send on the same PDF. If the recipient accepts an electronic document by email or through a portal, submit the validated file, not a screenshot of it or a scan of a printed copy.
The public service states the file-type and size limits, but the publicly available documentation does not comprehensively describe all internal criteria behind the result, such as the format of any technical report, revocation checks or the role of a timestamp. It would therefore be unwise to attribute checks to the portal that are not explicitly described.
What a valid result actually says
In ordinary terms, “valid” means that the uploaded file has passed the check performed by the service for a CEI signature. In practice, it indicates that the document and the signature applied to it should be considered together: the check is meaningful for that particular PDF, in that particular form.
European eIDAS rules use benchmarks for validating signatures including the integrity of the signed data and information about the certificate. It should not be assumed, however, that the HUB MAI portal publicly displays every criterion in the same technical form, or that its result resolves every issue in an application or case file.
| Question | What checking the PDF may clarify | What still needs to be checked separately |
|---|---|---|
| Is this the signed file? | It may support technical verification of the signature applied to that PDF. | Whether it is also the document required by the procedure, with all necessary pages and attachments. |
| Who signed it? | It may help associate the signature with the certificate used. | Whether the person had the necessary status, mandate or authority in the specific circumstances. |
| Is the document accepted? | It does not determine administrative or contractual acceptance. | The submission channel, form, deadline and signature type required by the recipient. |
A PDF may therefore pass the technical check and still be rejected in a process requiring a particular form, upload to its own portal, or a qualified signature. Conversely, a warning in a local application does not automatically prove that the file has been altered.
Why a signed PDF should not be saved again or scanned
An electronic signature is linked to the data in the document. Once it has been applied, any intervention in the PDF may affect the file’s verifiable integrity. There is no simple rule that every possible operation in a PDF editor must produce the same result in every application; it depends on the operation and on how the software changes the document. The safe practical rule remains: do not alter or save the PDF again after signing.
A scan of the printed document is no longer the electronic PDF that carries the verifiable signature. It may be useful only where a procedure expressly requires a scanned copy, but it cannot replace the original signed file for cryptographic verification.
Before sending the document, compare its filename, page count and size with the version checked. For high-stakes documents, keep the original in a separate folder and use only a copy for reading, without using that copy for submission.
An Adobe Acrobat warning does not automatically mean the document is false
In its guide to signing with a CEI, the Interior Ministry explains how to configure the RO CEI MAI RootCA root certificate in Adobe Acrobat. In other words, a locally installed PDF reader may not have the trust chain needed to immediately interpret the certificate as trusted.
This is why a warning displayed by Acrobat should be read carefully rather than immediately translated as “the PDF has been altered”. First check whether the application identifies a certificate-trust issue, a document-integrity issue, or another distinct message. If in doubt, check the same original PDF in HUB MAI.
The IDPLUGMANAGER application is primarily relevant when applying a signature with a CEI or when you need to view the certificate on the card. The Interior Ministry page lists version 4.5.0 for Windows, macOS and Linux, and recommends using a CEI-compatible reader. For simply checking an already signed PDF online, the card reader and application are not normally part of the portal upload process.
The CEI advanced signature is not a qualified signature
The electronic identity card contains a certificate for an advanced electronic signature issued by the Interior Ministry. Law No. 214/2024 provides that an advanced electronic signature created with a certificate issued by a Romanian public authority or institution may have the same legal effects as a handwritten signature, under the conditions laid down by law.
The wording “under the conditions laid down by law” matters. It does not automatically turn an advanced signature into a qualified signature or remove a procedure’s specific requirements. Public authorities and institutions have obligations concerning the receipt of electronic documents and the publication of the ways in which they may be received, but the reader must check the instructions of the service where the document is being filed.
A useful example is taxation: ANAF’s documentation for electronically submitted tax returns specifies the use of a qualified electronic signature. The ANAF procedure does not undermine the general legal value of the CEI advanced signature; it shows why validating a PDF and having it accepted in a specialised process are two different questions.
If the PDF is rejected, ask for the specific reason
Do not keep uploading the same file until the institution says precisely what it does not accept. A refusal may concern the file, the transmission channel, the type of signature, the form or the document’s content. These situations require different solutions.
- “File not accepted” or an upload error: check that it is a PDF and is under 20 MB for HUB MAI; for the recipient institution, check the limit and requirements of its portal.
- The signature is not recognised by the local application: check the exact message and the trusted-certificate configuration; do not alter the PDF to make the warning disappear.
- The institution says it does not accept the document: ask in writing for the procedural basis, the accepted signature type, the mandatory submission channel and whether its own form is required.
- A qualified signature is required: do not assume that a valid result from HUB MAI replaces that requirement. Ask for an explanation tied to the specific procedure.
- There is a dispute about the signature: retain the original PDF, the rejection message and any proof of transmission. Rules adopted by the Authority for the Digitalization of Romania in 2026 also address validation mechanisms for disputed or unrecognised advanced or simple signatures, but they do not automatically make the HUB MAI portal a qualified validation service.
For a private company, acceptance also depends on the contract, its internal policy and its technical tools. Request an answer before signing if the document is urgent or has significant effects.
What to keep with the document
For a simple request, the original PDF is often enough. For important documents, create a basic file containing the original signed document, proof of transmission, the date on which you checked it, the portal result if it can be saved, and replies received from the recipient.
The public documentation consulted for this guide does not provide a complete explanation of how files uploaded to the verification portal are retained or deleted. For this reason, do not upload documents other than the necessary PDF, and do not add extra data to it merely for testing. For questions about the processing or retention of the document, request clarification directly from the Interior Ministry.
Technical verification is a sound step before sending a document. But the right decision can be made only after separating the verdict on the file from the recipient’s rules: the PDF may be valid while the procedure still requires a different format, channel or type of signature.
Frequently asked questions
What files can I upload to the HUB MAI service for CEI verification?
The public interface of the dedicated CEI service says it accepts PDF files with a maximum size of 20 MB.
Do I need a card reader and IDPLUGMANAGER to check an already signed PDF?
To upload an already signed PDF to the online verification service, these are not normally part of the portal process. A compatible reader and IDPLUGMANAGER are chiefly needed to use the certificate on the CEI for signing or viewing.
Does a valid HUB MAI result require every institution to accept my document?
No. The result concerns the technical verification of the uploaded document. The institution may have its own procedure concerning the submission portal, format, attachments or required signature type.
Why does Adobe Acrobat say the signature is not trusted?
It may be a local configuration issue with the trust chain for the Interior Ministry certificate. The ministry’s guide explains installation of the RO CEI MAI RootCA root certificate; the warning must be read exactly and does not automatically prove that the document has been modified.
Sources consulted
- HUB MAI – Verification of a document electronically signed with a CEI
- HUB MAI – Guide to applying an electronic signature using a CEI
- Legislative Portal – Law No. 214/2024
- ANAF – Order No. 2213/2025, electronically submitted tax returns
- Legislative Portal – Authority for the Digitalization of Romania rule of 29 January 2026 on validation mechanisms






Discuția cititorilor
Ai o opinie sau o întrebare despre acest articol? Spune-ne ce crezi.
Fii primul care deschide discuția.
Te rugăm să păstrezi un limbaj civilizat și să discuți la subiect. Comentariile spam sunt filtrate automat.